Make identity, access and
delegated authority explicit across the systems you operate.
Zoiko Tech’s Identity & Access architecture is designed around trusted identities for people and systems, scoped authorization, least privilege, delegated authority, lifecycle control and evidence — so access decisions remain understandable and governable as the technology estate grows.
Home / Solutions / Identity & Access
Identity & AccessMake identity, access and delegated authority explicit across the systems you operate.
Zoiko Tech’s Identity & Access architecture is designed around trusted identities for people and systems, scoped authorization, least privilege, delegated authority, lifecycle control and evidence — so access decisions remain understandable and governable as the technology estate grows.
Explore Cybersecurity & Resilience →Identity-aware. Least-privilege by design. Delegation made explicit. Evidence preserved.
What do you need to control?
Choose a path and jump to the relevant part of the identity model.
What do you need to control?
Choose a path and jump to the relevant part of the identity model.
Why identity fragments
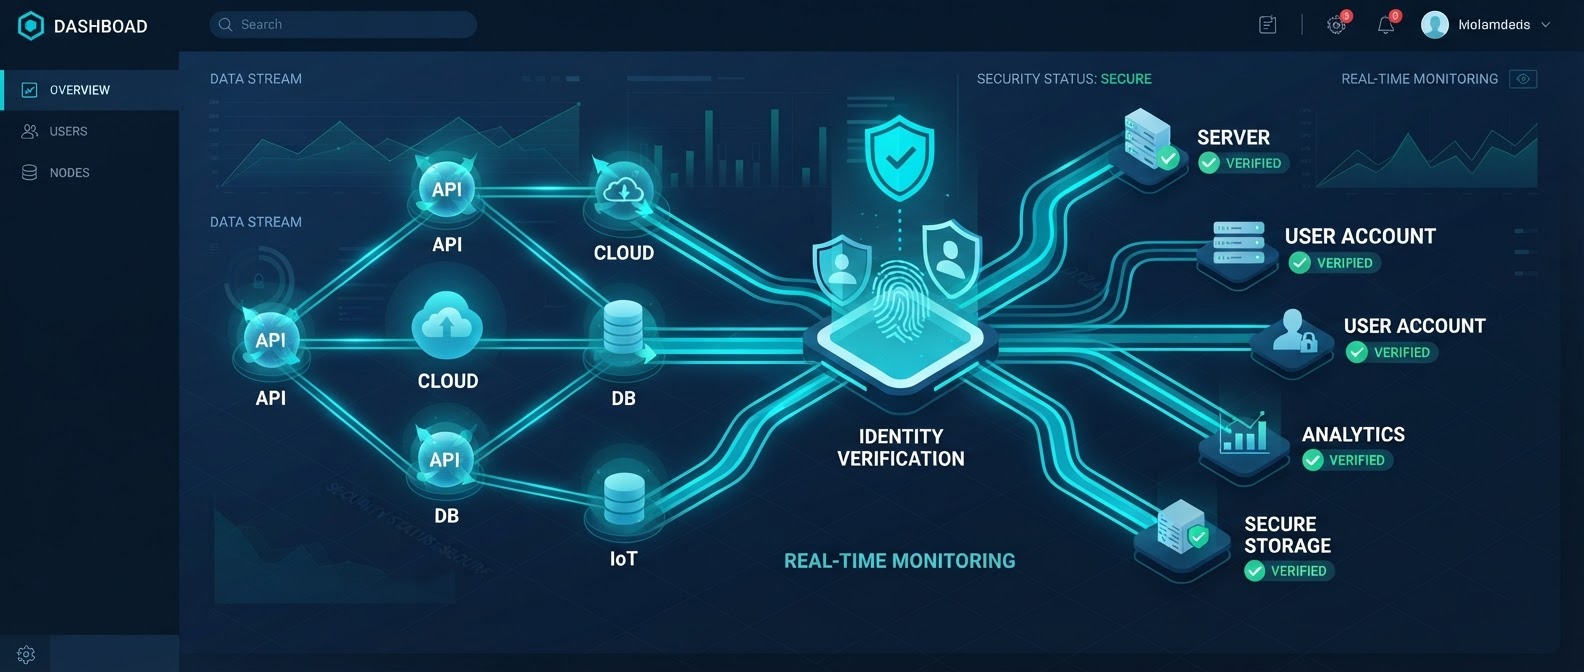
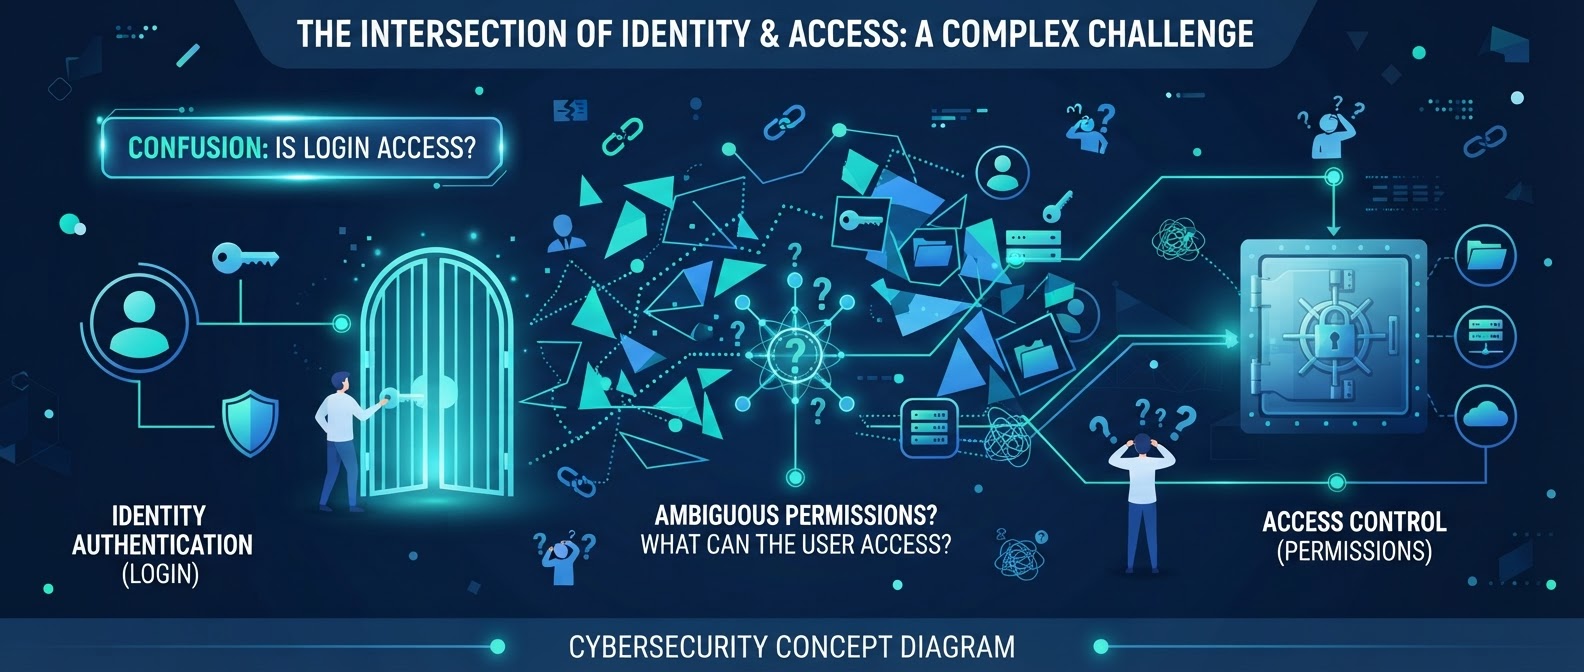
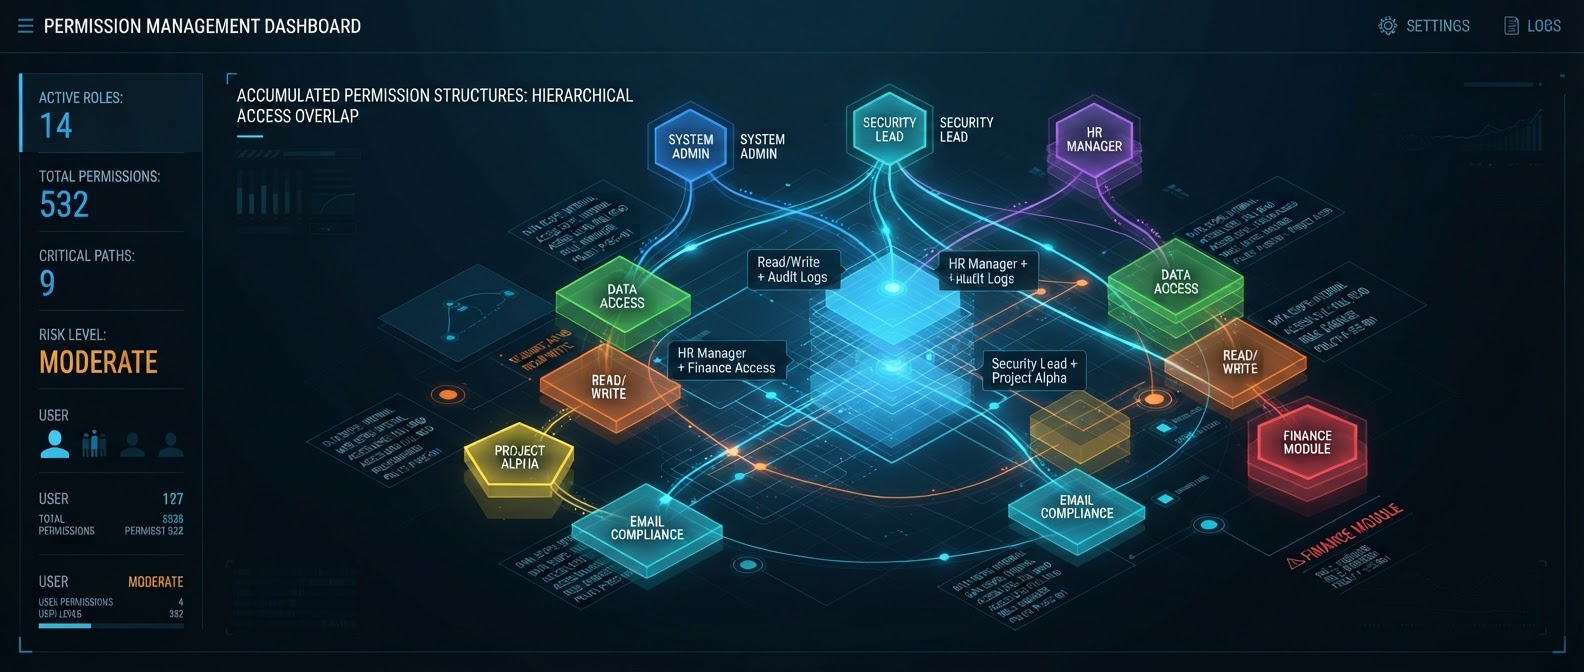
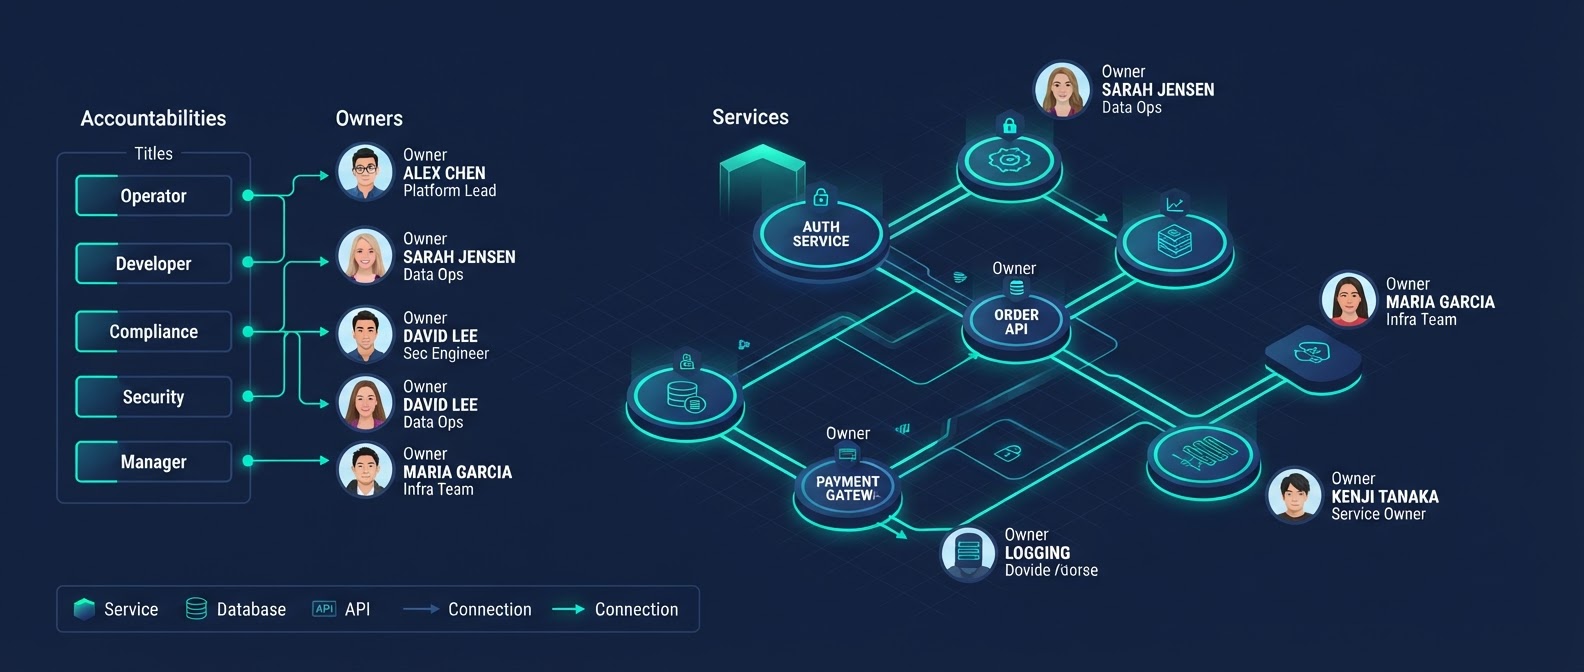
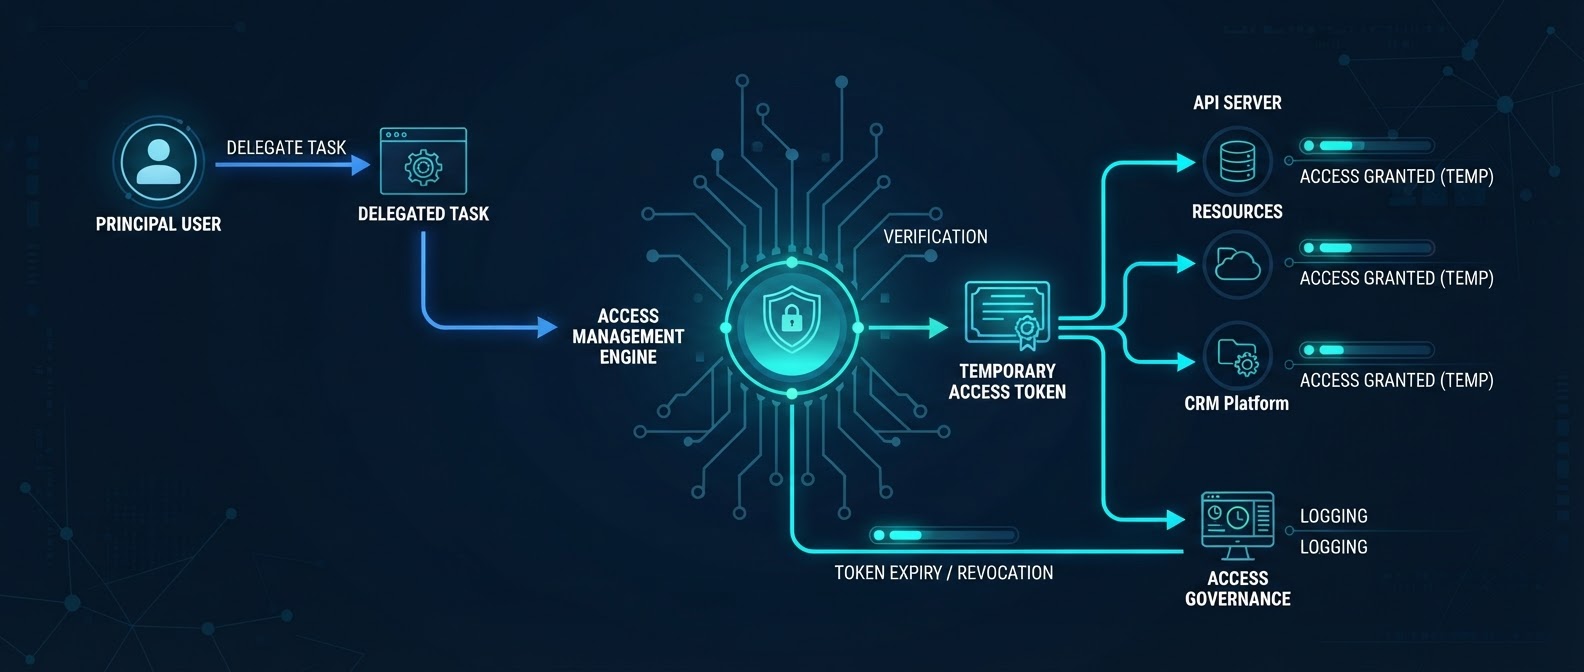
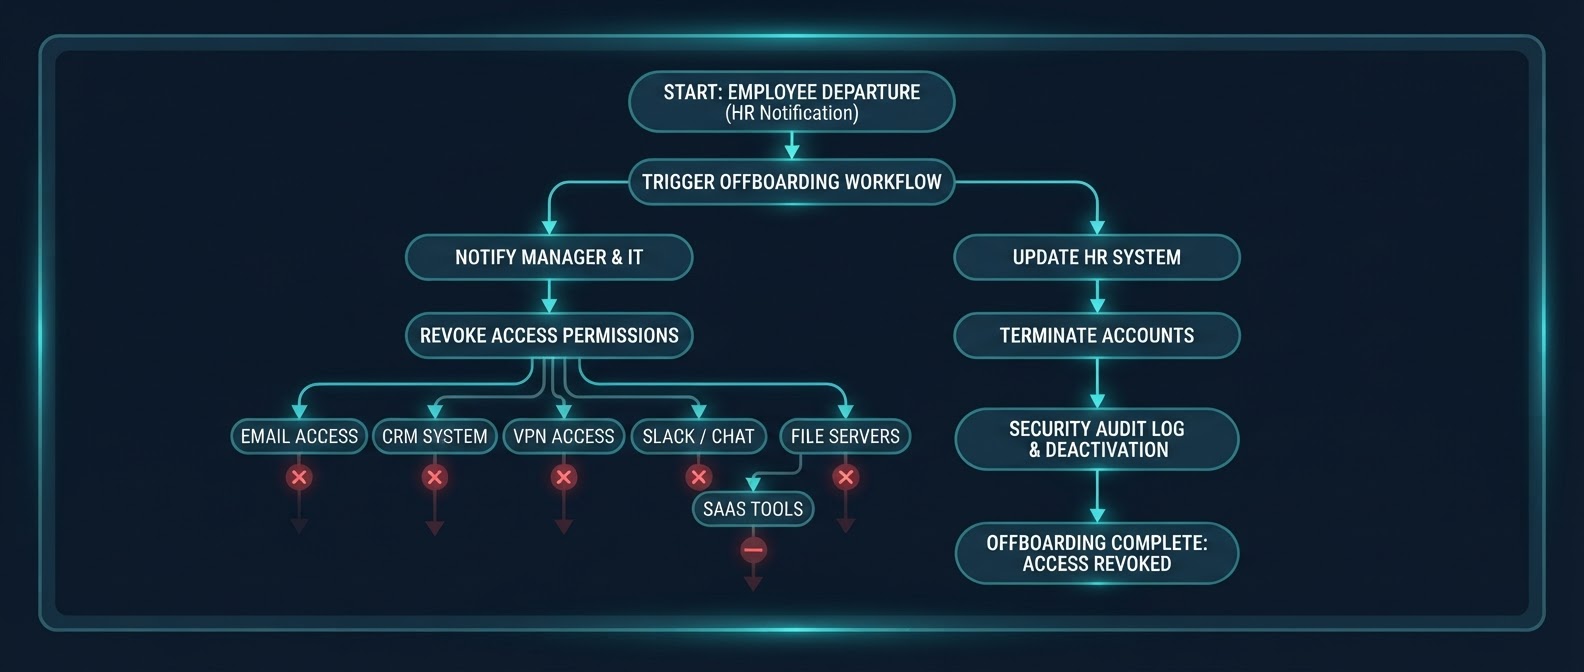
Why identity fragments
Identity and authority architecture
The access-decision chain, from who is acting to how authority is reviewed. Read from the bottom layer up.
Identity and authority architecture
The access-decision chain, from who is acting to how authority is reviewed. Read from the bottom layer up.
Architecture claims boundary. This is a recommended enterprise control model. Directory, federation, MFA, passkey, SCIM, policy-engine and session support must come from an approved Zoiko iD / Zoiko Access specification before it is represented as live.
Identity lifecycle
Authority changes as identities change. Each state has clear access behavior.
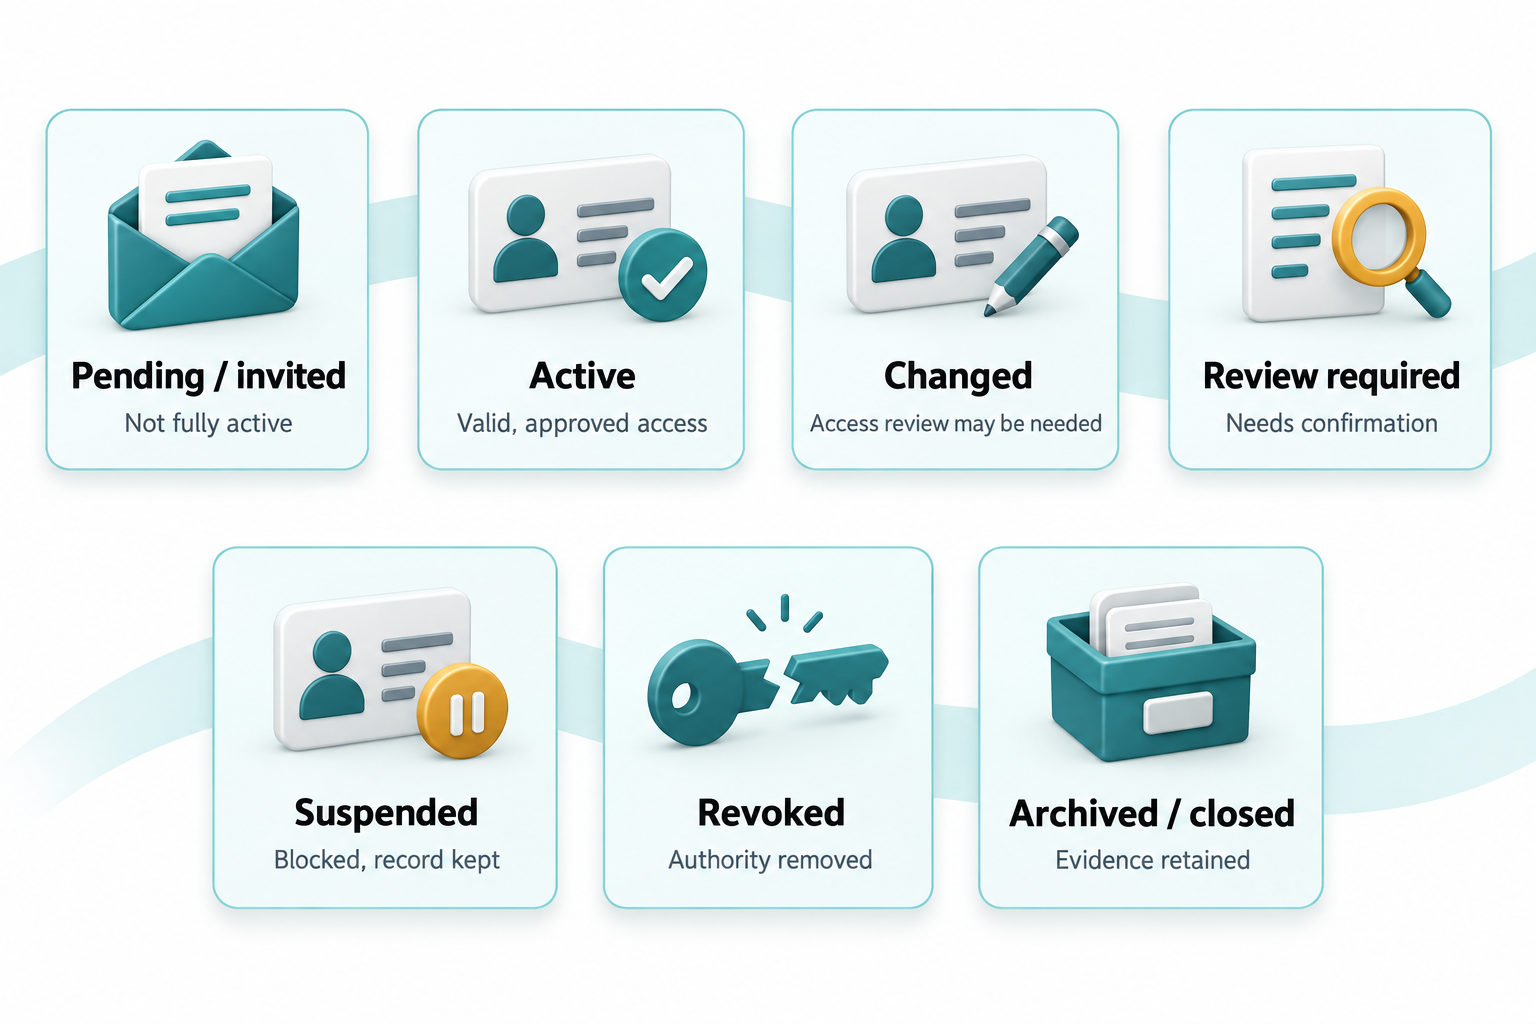
Identity lifecycle
Authority changes as identities change. Each state has clear access behavior.
Pending / invited
Not fully active
Active
Valid, approved access
Changed
Access review may be needed
Review required
Needs confirmation
Suspended
Blocked, record kept
Revoked
Authority removed
Archived / closed
Evidence retained
Identity detail (specimen data)
Identity
Type
Source
Owner
Status
Exception
Sample user A
User
Workforce
Manager
None
Sample service B
Service
Application
—
Sample partner C
External
Partner
Sponsor
Conflicting source
Authentication and session trust
Authentication is one layer of identity. The control objective comes first, and concrete methods appear only from current product documentation.

Identity source
The authoritative identity,
directory or account source.

Method
Only methods the product
officially supports.

Session
Active, expired, revoked or risk-
review states where supported.

Recovery
A high-risk flow that needs
explicit verification and audit.

Stronger assurance
An architecture concept for
sensitive actions, not a capability
claim.

Evidence
Time, assurance context and
result. Secrets are never
exposed.
Authentication and session trust
Authentication is one layer of identity. The control objective comes first, and concrete methods appear only from current product documentation.
Identity source
The authoritative identity,
directory or account source.
Method
Only methods the product
officially supports.
Session
Active, expired, revoked or risk-
review states where supported.
Recovery
A high-risk flow that needs
explicit verification and audit.
Stronger assurance
An architecture concept for
sensitive actions, not a capability
claim.
Evidence
Time, assurance context and
result. Secrets are never
exposed.
Copy rule. Modern identity is not a checklist of protocols or factors. No SSO, MFA or passkey support is claimed here.
Authorization and entitlements
Every access decision has a subject, a resource, an action, context, a policy and a result.
Decisions: allow, deny, approval required, step-up verification or exception path, as supported. Evidence shows why access exists, who granted it and when it expires.
Entitlement matrix (specimen data)
Principal
Resource
Entitlement
Scope
Grant source
Review / expiry
Sample user A (User)
Project workspace
Editor
One project
Group
Sample integration D
Reporting API
Read
Production
Direct
Sample agent E
Ticket queue
Approve
Team
Delegated
Delegated authority is its own object
Authority granted by one identity to another, for a defined purpose, scope and duration.
Delegator & delegate
Who grants authority and who
receives it.
Purpose & scope
Why it is needed, and the exact
resources and actions covered.
Duration
Start, expiry and renewal rules.
Approval & constraints
Required approver, environment,
action class or data limits.
Revocation
Immediate revoke or expiry,
removing downstream authority.
Evidence
Creation, approval, use, change
and revocation history.
Draft
Proposed
Approval required
Waiting
Active
Within scope
Expiring
Renewal review
Suspended
Disabled
Revoked
Ended early
Expired
Ended automatically
| Delegator | Delegate | Scope | Duration | State |
|---|---|---|---|---|
| Sample lead | Sample deputy | Approve requests, one team | Specimen dates | Active |
| Sample org X | Sample service | Read reports | Ended | Revoked |
Service, integration and agent identity
Systems must be authenticated as well as people. AI agents are governed identities with an accountable human owner.
Service / workload
Owner, purpose, environment,
permissions, rotation and review.
Integration
Owner, connected applications,
scopes, events and health.
API / automation client
Purpose, environment, scopes
and last-used state.
AI / agent
Named workflow, accountable
owner, allowed actions and
delegated authority.
Orphaned identity
No owner or dependency. Route
to review and revoke rather than
silently retain.
| Identity | Owner | Environment | Credential | Scope | Review |
|---|---|---|---|---|---|
| Sample agent E | Sample owner | Staging | Created · Last used · Expiry shown | Ticket queue | Due |
Credential-safety rule. Mockups never reveal keys, tokens, passwords or production identifiers.
Privileged and sensitive access
High-impact authority is kept separate from routine work. This is a recommended pattern; product support requires validation.
Privileged role
High-impact admin,
security, billing or
compliance authority.
Eligibility
Who may request or
hold it, and in what
scope.
Approval
Authorized approver
with rationale or
context.
Time / scope boundary
Temporary or bounded.
No JIT or PAM claim.
Sensitive action
Extra confirmation or
verification.
Review / revoke
Expiry and immediate
revoke path.
Evidence
Grant, use, approval and
revocation history.
| Requested authority | Scope | Duration | Approver | State |
|---|---|---|---|---|
| Billing administrator | One organization | Time-limited | Access approver | Approval required |
External and partner access
Temporary access and clear sponsorship by default. External access is never permanent unless someone decides it should be.
External identity
Partner, customer, contractor or
guest, with an internal sponsor.
Organization boundary
External company, tenant,
domain or relationship.
Resource scope
Only approved applications,
workspaces, APIs or data.
Duration & sponsor
Expiry or review defaults, and an
accountable internal role.
Policy
Domain, market, data and
workspace restrictions where
supported.
Offboarding
Revoke or expire when the
relationship or purpose ends.
Access review, evidence and exceptions
Review is continuous. Each item shows its access paths so nobody has to infer them.
Review decision
Keep, change, revoke, request
more evidence, or escalate.
Exception
Deviation with reason, owner,
approver and expiry.
Orphaned entitlement
No valid identity, resource or
owner. Routed to remediation.
Conflicting authority
Direct, group and delegated
paths shown together.
Evidence export
Where permitted, preserving
source, scope, time and
reviewer.
Audit timeline
Identity, role, entitlement,
delegation, review and revoke
events.
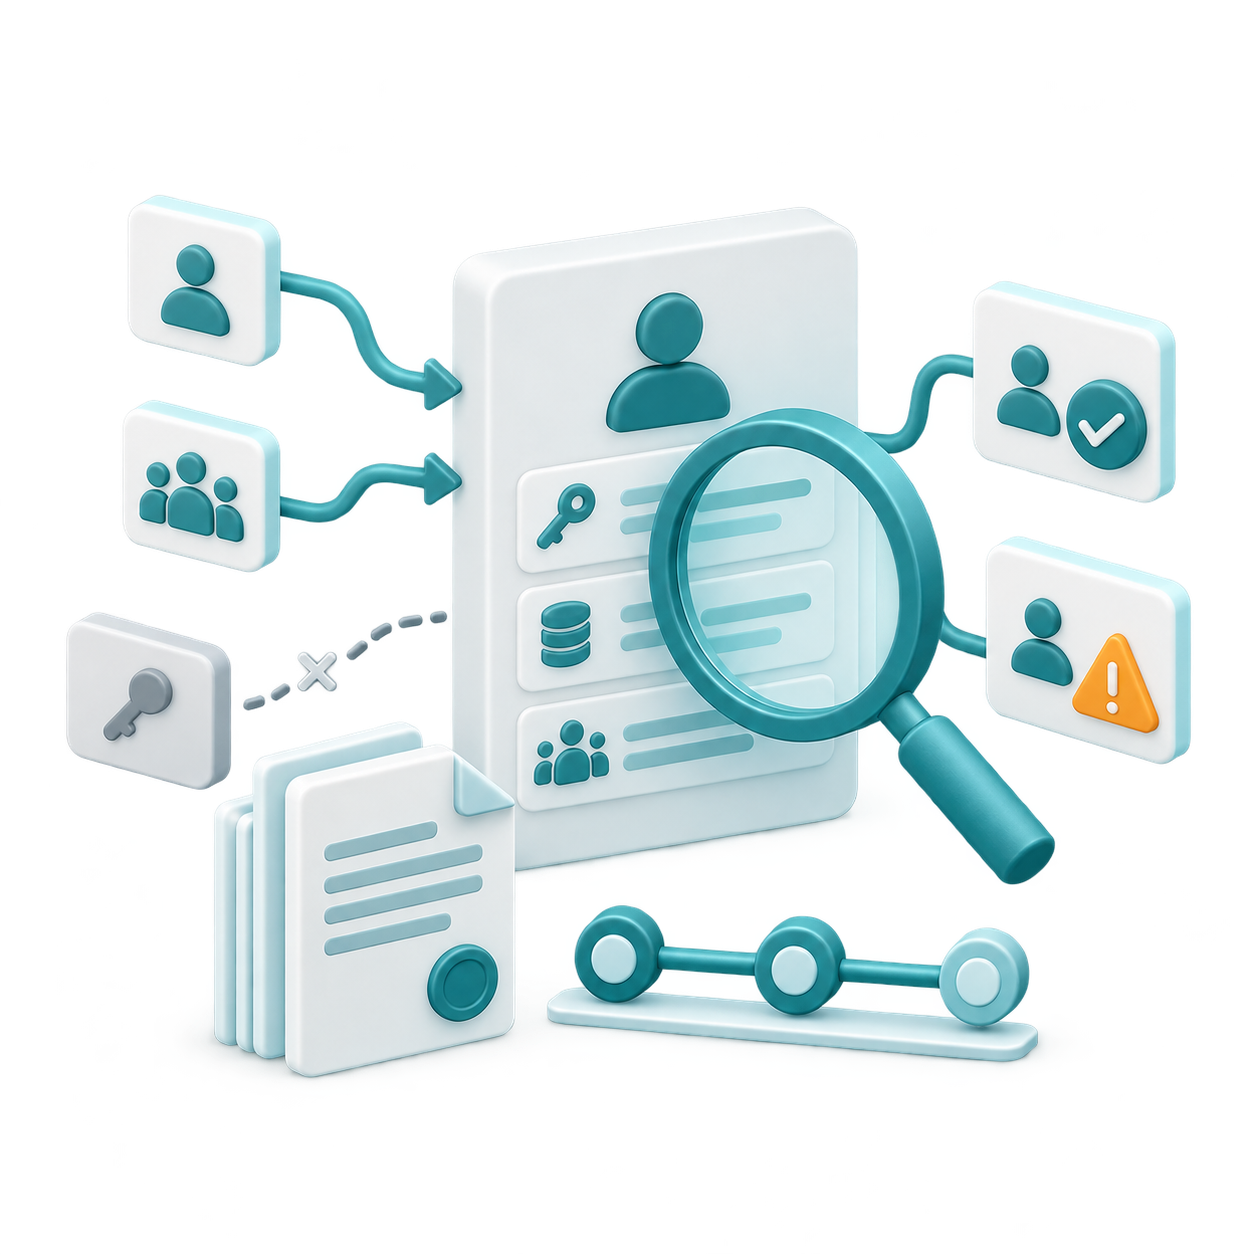
| Identity | Resource | Entitlement | Grant source | Owner | Decision |
|---|---|---|---|---|---|
| Sample user A | Project workspace | Editor | Group | Resource owner | Keep |
| Sample integration D | Reporting API | Read | Direct | Service owner | More evidence |
| Sample partner C | Shared workspace | Viewer | Delegated | — | Revoke |
Access review, evidence and exceptions
Review is continuous. Each item shows its access paths so nobody has to infer them.
Review decision
Keep, change, revoke, request
more evidence, or escalate.
Exception
Deviation with reason, owner,
approver and expiry.
Orphaned entitlement
No valid identity, resource or
owner. Routed to remediation.
Conflicting authority
Direct, group and delegated
paths shown together.
Evidence export
Where permitted, preserving
source, scope, time and
reviewer.
Audit timeline
Identity, role, entitlement,
delegation, review and revoke
events.
| Identity | Resource | Entitlement | Grant source | Owner | Decision |
|---|---|---|---|---|---|
| Sample user A | Project workspace | Editor | Group | Resource owner | Keep |
| Sample integration D | Reporting API | Read | Direct | Service owner | More evidence |
| Sample partner C | Shared workspace | Viewer | Delegated | — | Revoke |
Platform evidence, gated by launch readiness
Named products appear only when their public destination, descriptor, maturity and capabilities are approved. Until then this page is architecture-first, and there are no empty product cards.

Identity technology
Identity, authentication,
entitlement and delegated
authority as a technology pillar.

Access governance
Scoped authority, review and
revocation as a control model.
Zoiko iD / Zoiko Access
Mapped delivery evidence when
launch-ready.

Trust Center / Cybersecurity
Authoritative security and trust
evidence.
Platform evidence, gated by launch readiness
Named products appear only when their public destination, descriptor, maturity and capabilities are approved. Until then this page is architecture-first, and there are no empty product cards.
Identity technology
Identity, authentication,
entitlement and delegated
authority as a technology pillar.
Access governance
Scoped authority, review and
revocation as a control model.
Zoiko iD / Zoiko Access
Mapped delivery evidence when
launch-ready.
Trust Center / Cybersecurity
Authoritative security and trust
evidence.
Integration and developer layer
Only approved, documented integrations are shown. No protocol support is implied.
Identity sources
Approved workforce, directory,
customer or partner sources.
Applications
Zoiko and external resources
receiving identity context.
APIs / events
Lifecycle, role or access events
where supported.
Federation
Exact methods only from
authoritative documentation.
Provisioning
Only if publicly supported.
Audit
Change and decision evidence at
the level the product exposes.
Start bounded, then expand

Define scope
People, externals,
services, agents, apps,
owners.
Scope approved

Map sources
Authoritative records,
relationships, conflicts.
Source model approved
Design authority
Roles, entitlements,
delegation, privilege,
lifecycle.
Authority model approved

Integrate & validate
Bounded systems; test
success and denial
paths.
Acceptance met

Pilot
Limited users, services
and applications.
Pilot reviewed

Roll out
Expand while monitoring
exceptions.
Readiness confirmed

Review continuously
Reviews, orphans,
exceptions, evidence.
Review completed
Start bounded, then expand
Define scope
People, externals,
services, agents, apps,
owners.
Scope approved
Map sources
Authoritative records,
relationships, conflicts.
Source model approved
Design authority
Roles, entitlements,
delegation, privilege,
lifecycle.
Authority model approved
Integrate & validate
Bounded systems; test
success and denial
paths.
Acceptance met
Pilot
Limited users, services
and applications.
Pilot reviewed
Roll out
Expand while monitoring
exceptions.
Readiness confirmed
Review continuously
Reviews, orphans,
exceptions, evidence.
Review completed
Technology in practice
Proof appears only when approved for public use.
Identity architecture
Estate, problem, model,
governance, approved result.
Access governance
Review issue, lifecycle model,
approved outcome.
Delegation
Need, scope, approval, expiry,
outcome.
Machine identity
Ownership, scope, credential and
review design.
Technology in practice
Proof appears only when approved for public use.
Identity architecture
Estate, problem, model, governance,
approved result.
Access governance
Review issue, lifecycle model, approved
outcome.
Delegation
Need, scope, approval, expiry, outcome.
Evidence pendingMachine identity
Ownership, scope, credential and review
design.
No approved public proof yet? Talk to us about the architecture, launch-readiness labels and Trust Center. We don’t publish authentication success rates, risk reductions, logos or compliance claims without evidence.
Where teams go next
Adjacent routes are contextual, and never interrupt an access review, revocation or privileged flow.
Identity foundation
Cybersecurity & Resilience,
Regulatory & Compliance,
platform administration.
AI / agent deployment
AI Governance & Assurance, then
agent authority here.
Developer platform
Cloud & Developer Infrastructure,
Modernization & Integration.
Workforce systems
Workforce & Productivity, HR,
Payroll & Revenue Operations.
Regulated environments
Regulatory & Compliance,
Cybersecurity & Resilience.